Business 4 min read By Alice Ashford
Hackers Drain $6.3 Billion From Binance Via Engineer Phishing
Hackers drained $6.3 billion from the world's largest crypto exchange, and shortly afterward the French bank Crédit Mutuel Arkéa reported the theft of about 100 million euros. Regulators and the industry see shared weak points in these incidents that also concern European banks.
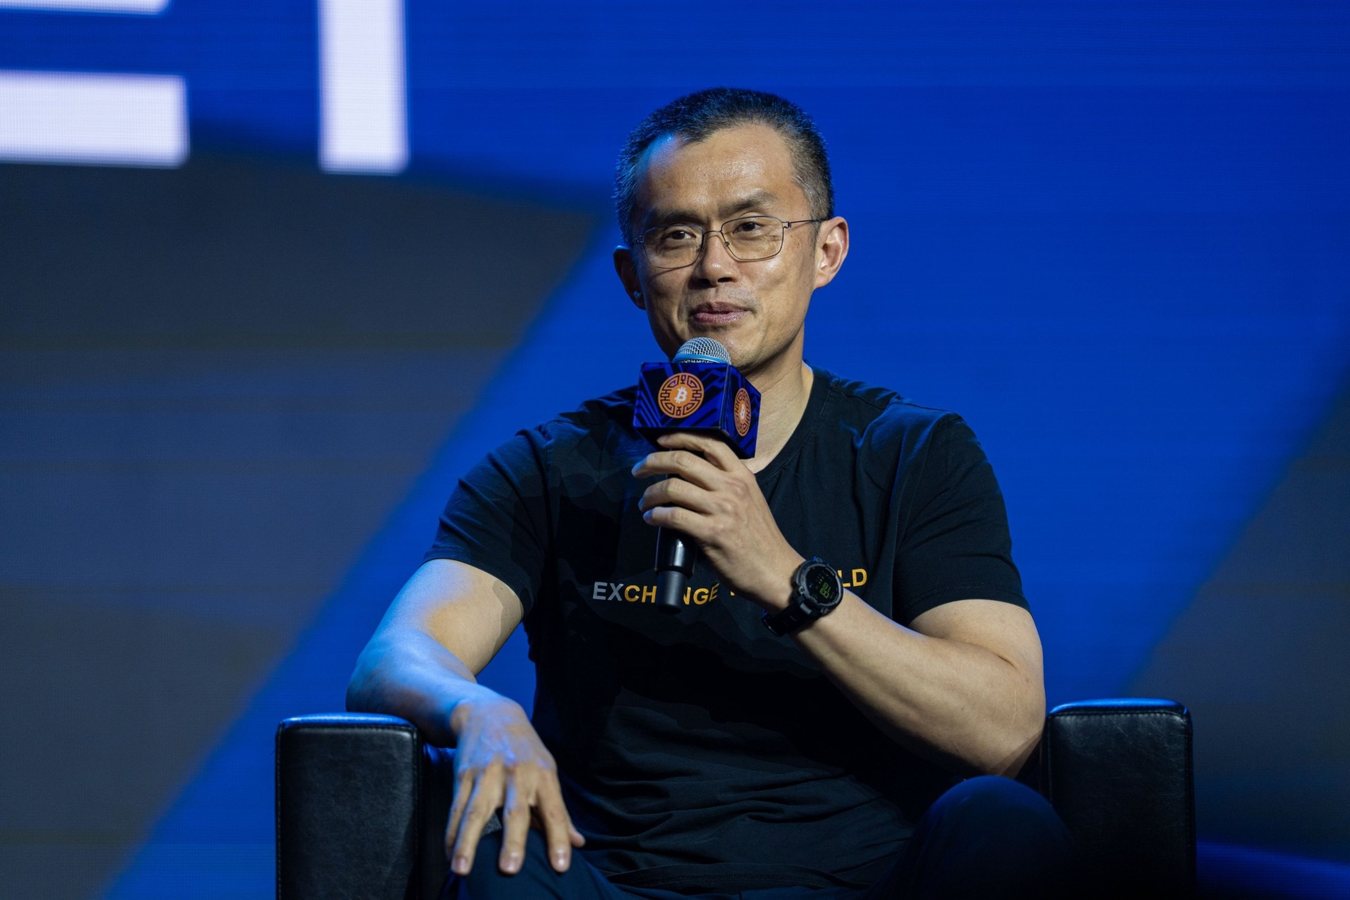
Hackers drained $6.3 billion from Binance, the world's largest cryptocurrency exchange, on October 29. The attack relied on social engineering and malicious software that reached the computer of one of the company's engineers. According to reports, the engineer was lured by fake job interviews, and during them he installed a malicious program. The US Federal Bureau of Investigation seized $1.2 billion of the stolen funds. Binance says it has recovered about 98% of the losses.
Less than a week after the Binance incident, the French bank Crédit Mutuel Arkéa announced a similar problem. It said attackers had stolen about 100 million euros ($112 million). The hackers used the institution's own bank account to carry out transactions. Access, according to the bank, was obtained through a service provider whose name the bank did not disclose. The institution assured customers that the incident did not affect their assets, meaning, in its words, that their funds were not harmed.
The comparison of the two cases is causing concern in the banking sector. The chief executive of Global Settlement said that an average bank cannot remain secure under current conditions. The former CEO of Binance believes banks are in an even worse position than crypto platforms. He explains that banks can block or reverse payments, whereas crypto platforms mostly do not have such capabilities. At the same time, researchers stress that regulatory compliance alone does not guarantee security.
Regulators are already responding. On November 2, the US Federal Reserve and the Office of the Comptroller of the Currency began calling banks to ask about unusual activity and service disruptions. Back in July, the European Central Bank warned 110 bank executives about the risks posed by advanced artificial intelligence. In the EU, the DORA rules on the operational resilience of digital systems in the financial sector have applied since January 2025, including requirements for managing risks related to IT infrastructure and external providers.
Experts point to several weak points common to many banks. The first is long chains of external providers through which attackers can penetrate. The second is outdated core technological infrastructure that still underpins the operations of many institutions. Separately, they mention connected devices without updates, which attackers have taken over in supermarkets and blood banks. Such cases show that vulnerabilities can exist even where security is not regarded as a main priority.
A separate topic is AI agents, which consumers increasingly use to make payments. Citigroup and Bank of America are restricting such agents' access to accounts. Jamie Dimon of JPMorgan has called for refraining from autonomous AI-initiated payments. Several British banks have already blocked AI agents, while Santander and ING allow their use within limits set by the customer. The banks' differing approaches show that the industry has not yet decided how to combine the convenience of automation with control over accounts.
Source: fortune.com
6